Cloud Security
Cloud Cryptojacking: Warning Signs and Immediate Response Steps
Resource spikes in cloud environments often indicate unauthorized mining processes that evade standard monitoring by mimicking legitimate workload patterns.
Resource spikes in cloud environments often indicate unauthorized mining processes that evade standard monitoring by mimicking legitimate workload patterns.
Fraud alerts create a mandatory pause in account opening, forcing verification before thieves can exploit stolen credentials for new credit.
AI agents can bypass traditional firewalls by executing actions that appear human, making perimeter defenses insufficient for containing autonomous decision-making errors.
Traditional email filters fail here because the attacker intercepts and modifies messages in real-time, creating a seamless loop that bypasses standard authentication checks.
Logic bombs hide in plain sight, waiting for a specific condition to trigger destruction rather than executing immediately upon infection.
Detecting AI text relies on statistical patterns rather than truth, meaning even the best tools miss sophisticated edits and cannot verify factual accuracy.
Your usage policy fails when it ignores the invisible data exfiltration that happens before the model ever generates a response, exposing proprietary logic to public training sets.
Search engine optimization poisoning rarely targets your domain directly; it hijacks the trust users place in search results to redirect them to malicious infrastructure you do not control.
Network scanning reveals hidden entry points by testing every connection, turning invisible infrastructure into a target list for attackers.
Most users lose access to their accounts because they store backup codes insecurely, not because attackers bypass the security layer directly.
Most organizations fail not because they lack tools, but because they lack pre-defined decision trees for containment actions during high stress.
Information sharing and analysis centers transform raw alerts into actionable context, allowing you to defend against threats before they reach your perimeter.
Moving security checks to the earliest development stages reveals flaws before they compile, but it also slows down the deployment pipeline if the tooling is not tuned for speed.
Most web vulnerabilities stem from browser behavior rather than server flaws, and headers dictate how the browser interprets and restricts your content.
Private browsing deletes local history but does not hide your activity from networks, websites, or your internet service provider.
AI agents differ from chatbots by acting on your behalf, creating security gaps that standard access controls cannot easily monitor or restrict.
Most organizations focus on strengthening walls, but true security comes from removing the doors and windows that attackers use to enter your digital property.
Your website’s analytics tools may trigger consumer privacy rights even if you never collect personal data directly from your users.
Data residency controls physical location, not just legal jurisdiction, creating hidden latency costs and complex backup strategies for distributed teams.
Email authentication protocols verify sender identity at the protocol level, preventing attackers from spoofing your domain in phishing campaigns.
Mobile malware often hides inside legitimate-looking applications and exploits permission models rather than relying on obvious visual warnings or system crashes.
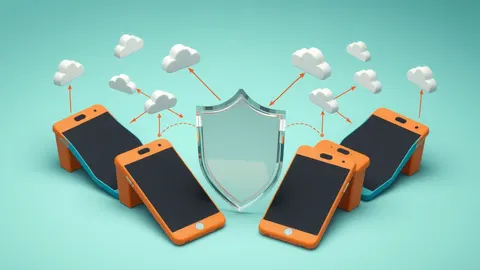
Cloud Access Security Brokers enforce policies between users and cloud services, preventing data leaks even when employees use personal devices or shadow IT applications.
Policies often exclude losses from poor log retention or missing incident communication plans, turning coverage into a hollow promise during a crisis.
IDOR flaws let users access private data by simply changing a number in the URL, often bypassing standard login screens without triggering any alerts.