Threat Intelligence
Threat Hunting Cyber Security: Proactive Detection That Alerts Miss
Manual threat hunting finds hidden compromises that automated tools ignore by searching for behavioral anomalies rather than known signatures.
The InfoSec Ledger Explainers Desk is the part of the InfoSec Ledger newsroom that covers reference guides that explain the ideas behind the headlines. It is a newsroom desk, not a single person. Sections: Guides. Guides are drafted with AI assistance, carry no invented statistics and are reviewed when the facts change. It has published 84 articles so far. See the editorial policy or report an error.
Manual threat hunting finds hidden compromises that automated tools ignore by searching for behavioral anomalies rather than known signatures.
Firewalls filter traffic by rules, while intrusion prevention systems inspect packet contents to stop active exploits before they execute on your servers.

Mass assignment flaws let attackers rewrite hidden data fields by submitting extra parameters in standard web forms, often bypassing basic input validation entirely.
Server-side template injection lets attackers execute code by tricking the server into rendering malicious input as part of a web page template.
An SBOM reveals hidden third-party components in your software, exposing supply chain risks that standard security checks often miss.

Treating AI agents like static users ignores their ability to escalate privileges through context, creating hidden data exfiltration paths that standard firewalls miss.
Most breaches occur because organizations wait for vendor patches instead of isolating vulnerable systems immediately upon discovery.
A single misconfigured permission can allow a low-level user to seize full administrative control of your entire network infrastructure.
Automated language models remove the grammatical errors that traditionally signal fraud, forcing you to verify identity through out-of-band channels rather than reading text carefully.
AI agents execute actions autonomously, turning a single compromised credential into a chain of unauthorized transactions that standard firewalls cannot stop.
Information-flow control stops data leakage by tagging every byte, ensuring sensitive inputs never mix with public outputs in autonomous systems.
Patching is a single remediation step, whereas vulnerability management is the continuous cycle of identifying, prioritizing, and treating all security weaknesses.
Misconfigured routing tables and legacy protocols in application delivery controllers allow attackers to bypass authentication entirely without brute-forcing credentials.
Automated scripts generate more web traffic than humans, masking data theft behind legitimate-looking requests that standard filters miss.
Standard user permissions fail for AI agents because these systems execute actions at speeds humans cannot monitor, requiring new identity and boundary management strategies.
Physical access controls fail when staff ignore social dynamics, allowing unauthorized entry that bypasses digital defenses and grants direct system access.
The framework maps adversary behavior rather than specific tools, allowing you to detect attacks even when criminals change their software or techniques.
True anonymization fails because modern re-identification techniques can link stripped data points back to specific individuals with alarming accuracy.
Privacy by Design shifts security from a final audit step to the first line of code, preventing data leaks before the product even launches.
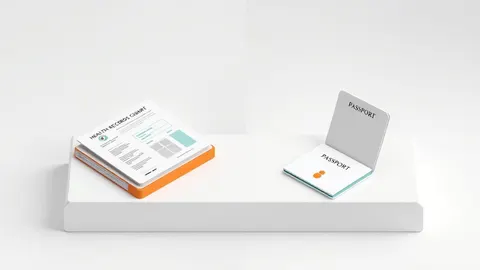
These frameworks protect different data types with distinct scopes, requiring separate compliance strategies even when systems overlap in a single organization.
Policy evaluation happens at authentication time, meaning a single misconfigured rule can block legitimate users or leave critical assets exposed to credential theft.
Unauthorized access often succeeds not by breaking encryption, but by exploiting the trust relationships between systems that handle different data types.
Synthetic media uses algorithms to generate realistic audio and video, creating a verification crisis that challenges your ability to trust digital evidence.
Granting location access to a flashlight app creates a persistent tracking vector that survives device resets and complicates data deletion requests.