Threat Intelligence
What Is MITRE ATT&CK Framework Used For: Practical Defense Mapping
The framework maps adversary behavior rather than specific tools, allowing you to detect attacks even when criminals change their software or techniques.
Threat Intelligence coverage from InfoSec Ledger holds 8 articles, 8 of them reference guides. The newest was published on October 12, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include CISA Cybersecurity Advisories and FIRST: Forum of Incident Response and Security Teams.
The framework maps adversary behavior rather than specific tools, allowing you to detect attacks even when criminals change their software or techniques.
Network scanning reveals hidden entry points by testing every connection, turning invisible infrastructure into a target list for attackers.
Information sharing and analysis centers transform raw alerts into actionable context, allowing you to defend against threats before they reach your perimeter.
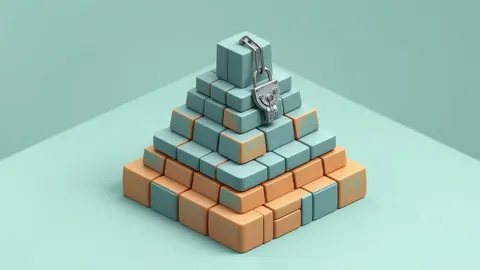
Blocking surface-level indicators provides false security because attackers change them instantly, while targeting their methods forces costly operational shifts.
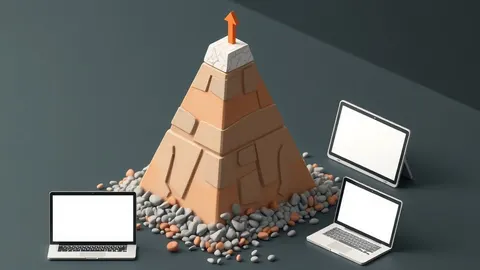
The lowest layers of the threat model are cheap for attackers to change, while the highest layers force them to rebuild their entire operation from scratch.
Keeping logs forever increases your attack surface and legal liability while providing diminishing returns for incident response.
Detection engineering reveals that most alerts fail not because of missing tools, but because the underlying data lacks the context needed to distinguish noise from noise.
See how attackers extract login tokens from your computer’s active memory and the specific steps to stop them from reusing your access.