Malware & Ransomware
Logic Bombs: The Silent Trigger Mechanism Inside Your Systems
Logic bombs hide in plain sight, waiting for a specific condition to trigger destruction rather than executing immediately upon infection.
Malware & Ransomware coverage from InfoSec Ledger holds 7 articles, 7 of them reference guides. The newest was published on October 9, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include CISA: Stop Ransomware and MITRE ATT&CK.
Logic bombs hide in plain sight, waiting for a specific condition to trigger destruction rather than executing immediately upon infection.
Search engine optimization poisoning rarely targets your domain directly; it hijacks the trust users place in search results to redirect them to malicious infrastructure you do not control.
Mobile malware often hides inside legitimate-looking applications and exploits permission models rather than relying on obvious visual warnings or system crashes.
Scareware bypasses technical defenses by exploiting human fear, using fake system alerts to force immediate action before logic can intervene.
Browser hijackers often hide inside legitimate browser extensions, making them invisible to standard antivirus scans that only check installed applications.
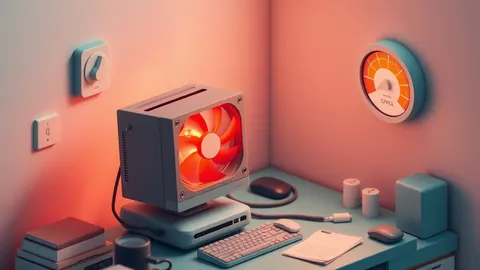
Most cryptojacking infections leave no file traces, making power bills and fan noise the only reliable early indicators of a compromised system.
File hashes create unique digital fingerprints that detect exact malware copies, but they fail against modified code or polymorphic threats that change their appearance.