Data Breaches
Cyber Insurance for Small Teams: Coverage Gaps and Cost Control
Policies often exclude losses from poor log retention or missing incident communication plans, turning coverage into a hollow promise during a crisis.
Policies often exclude losses from poor log retention or missing incident communication plans, turning coverage into a hollow promise during a crisis.
IDOR flaws let users access private data by simply changing a number in the URL, often bypassing standard login screens without triggering any alerts.
Blocking surface-level indicators provides false security because attackers change them instantly, while targeting their methods forces costly operational shifts.
Browser tracking scripts often bypass basic firewalls, silently mapping your customer’s behavior and exposing your network to subtle data leaks.
Fine-tuning adapts a general model to your specific data, creating a specialized tool that outperforms generic prompts in narrow tasks.
Scareware bypasses technical defenses by exploiting human fear, using fake system alerts to force immediate action before logic can intervene.
People search sites leave distinct DNS and HTTP headers that reveal data scraping before any personal information leaves your network perimeter.
Leaving the Kubernetes dashboard open to the internet grants attackers direct control over your entire cluster infrastructure immediately.
An incident response plan turns chaotic technical alerts into a coordinated legal and operational recovery, preventing minor breaches from becoming existential threats.
Cloud incident response shifts from containing physical networks to isolating ephemeral resources and managing shared liability across provider boundaries.
Reconnecting infected devices to the network before isolating them allows the botnet controller to map your entire internal infrastructure and accelerate lateral movement.
Most policy failures stem from ignoring the hidden cost of context leakage, not from a lack of technical controls or employee intent.
Hardcoded credentials often survive code reviews because they resemble valid configuration strings, requiring pattern matching rather than human inspection to uncover.
Browser hijackers often hide inside legitimate browser extensions, making them invisible to standard antivirus scans that only check installed applications.
Bias rarely originates in code logic. It accumulates silently through data selection and feedback loops that reinforce historical inequalities long before deployment.
Synthetic audio attacks succeed not through Hollywood-quality realism, but by exploiting human trust in familiar voices and bypassing outdated verification habits.
Most secure file sharing failures stem from weak access controls and encrypted local copies, not from the transport channel itself.
Small businesses face legal exposure because third-party cookies often track employee behavior on company networks without explicit consent mechanisms.
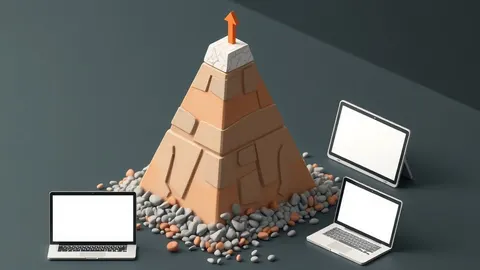
The lowest layers of the threat model are cheap for attackers to change, while the highest layers force them to rebuild their entire operation from scratch.
Most cryptojacking infections leave no file traces, making power bills and fan noise the only reliable early indicators of a compromised system.
Session cookies grant immediate access without passwords, meaning a single stolen token bypasses most multi-factor authentication controls entirely.
Unlike a PIN, biometric data cannot be changed if stolen, turning a convenient shortcut into a permanent identity risk that persists across all services.
Connecting an AI agent to your internal systems creates a new attack surface that traditional perimeter defenses cannot see or block.
Most IoT device failures are silent protocol leaks that bypass visual indicators, requiring network-level inspection rather than user interface monitoring for detection.