Cyber Attacks
Conditional Access Policies Best Practices for Secure Identity
Policy evaluation happens at authentication time, meaning a single misconfigured rule can block legitimate users or leave critical assets exposed to credential theft.
Everything InfoSec Ledger has reported about cloud security: 8 stories, newest first. Part of our Cloud Security coverage.
Policy evaluation happens at authentication time, meaning a single misconfigured rule can block legitimate users or leave critical assets exposed to credential theft.
Resource spikes in cloud environments often indicate unauthorized mining processes that evade standard monitoring by mimicking legitimate workload patterns.
Data residency controls physical location, not just legal jurisdiction, creating hidden latency costs and complex backup strategies for distributed teams.
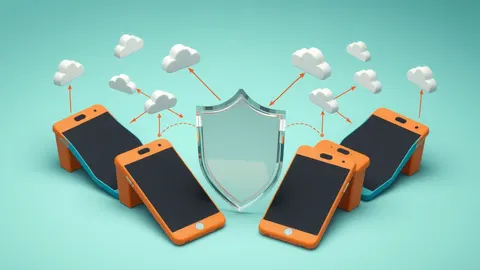
Cloud Access Security Brokers enforce policies between users and cloud services, preventing data leaks even when employees use personal devices or shadow IT applications.
Cloud incident response shifts from containing physical networks to isolating ephemeral resources and managing shared liability across provider boundaries.
Hardcoded credentials often survive code reviews because they resemble valid configuration strings, requiring pattern matching rather than human inspection to uncover.
Cloud-native security fails when organizations treat dynamic infrastructure like static servers, ignoring the ephemeral nature of containers and the complexity of distributed identity.
A landing zone is not a one-time setup but a dynamic baseline that prevents configuration drift from creating invisible security gaps across your cloud accounts.